Sightic Access

Iris and face authentication for secure access, in under one second.

Right person.
Right access.
At all times.

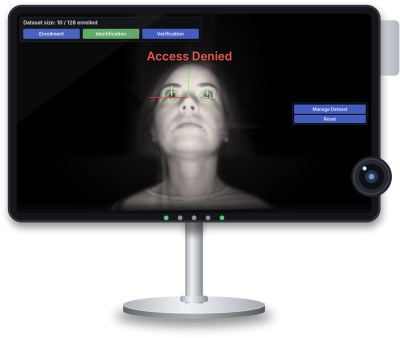
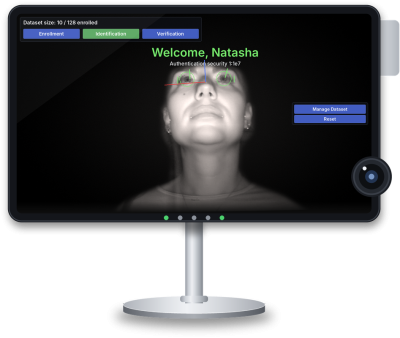
Sightic Access combines iris and face recognition to verify that the right person gets access to the right environment or system. Verification takes less than one second and requires no physical contact. The multimodal combination of iris and face gives a false match rate of 1 in 1 billion.

Verify the person, not just the card.
Biometrics are tied to the individual. They cannot be lost, stolen or lent out like a keycard. At a computer, the system can also continuously confirm that the same authorized person is still in front of the screen and working.

How it works.

1. Approach

Recognition starts as the person approaches the access point, and accuracy increases as they get closer.

2. Verify

Face and iris are checked together in one multimodal authentication.

3. Decide

Authorized persons are verified in under a second.

sightic-kiosk-denied-landscape-small_1
sightic-kiosk-screen-landscape-small_2

Security you can measure.

Face and iris recognition combined in one contactless check. Works with glasses, masks, beards and headwear.

<1 second

verification.

1 in 1,000,000,000

false match rate (face + iris)

500,000+

vehicles already running the technology.

Built for real conditions with proven technology.

Sightic Access recognizes people as they actually look: with glasses, masks, makeup, beards or headwear. Continuous verification also confirms that the same authorized person stays in front of the screen, with no extra steps for the user.

The technology isn’t new to the field. It already runs in more than 500,000 vehicles worldwide and builds on Smart Eye’s 25+ years of experience in eye tracking.
Who it’s for?

Sightic Access is designed for restricted areas, secure facilities and safety-critical environments, including operators of vehicles and heavy machinery.

Privacy by design.

Sightic is built on data minimization and on-device processing. No biometric data is stored, transmitted or shared. The architecture is designed to meet EU GDPR requirements and is audited against ISO 27001 and ISO 9001.

Get In Touch.

Want to see it in action? Contact us for a demo.

Let's get in contact

No matter what drives you, we would like to hear from you.